LAHORE – A compromised HBO Max advertising account was used to distribute malicious advertisements on Reddit, exposing users to a growing cyberattack technique known as ClickFix.
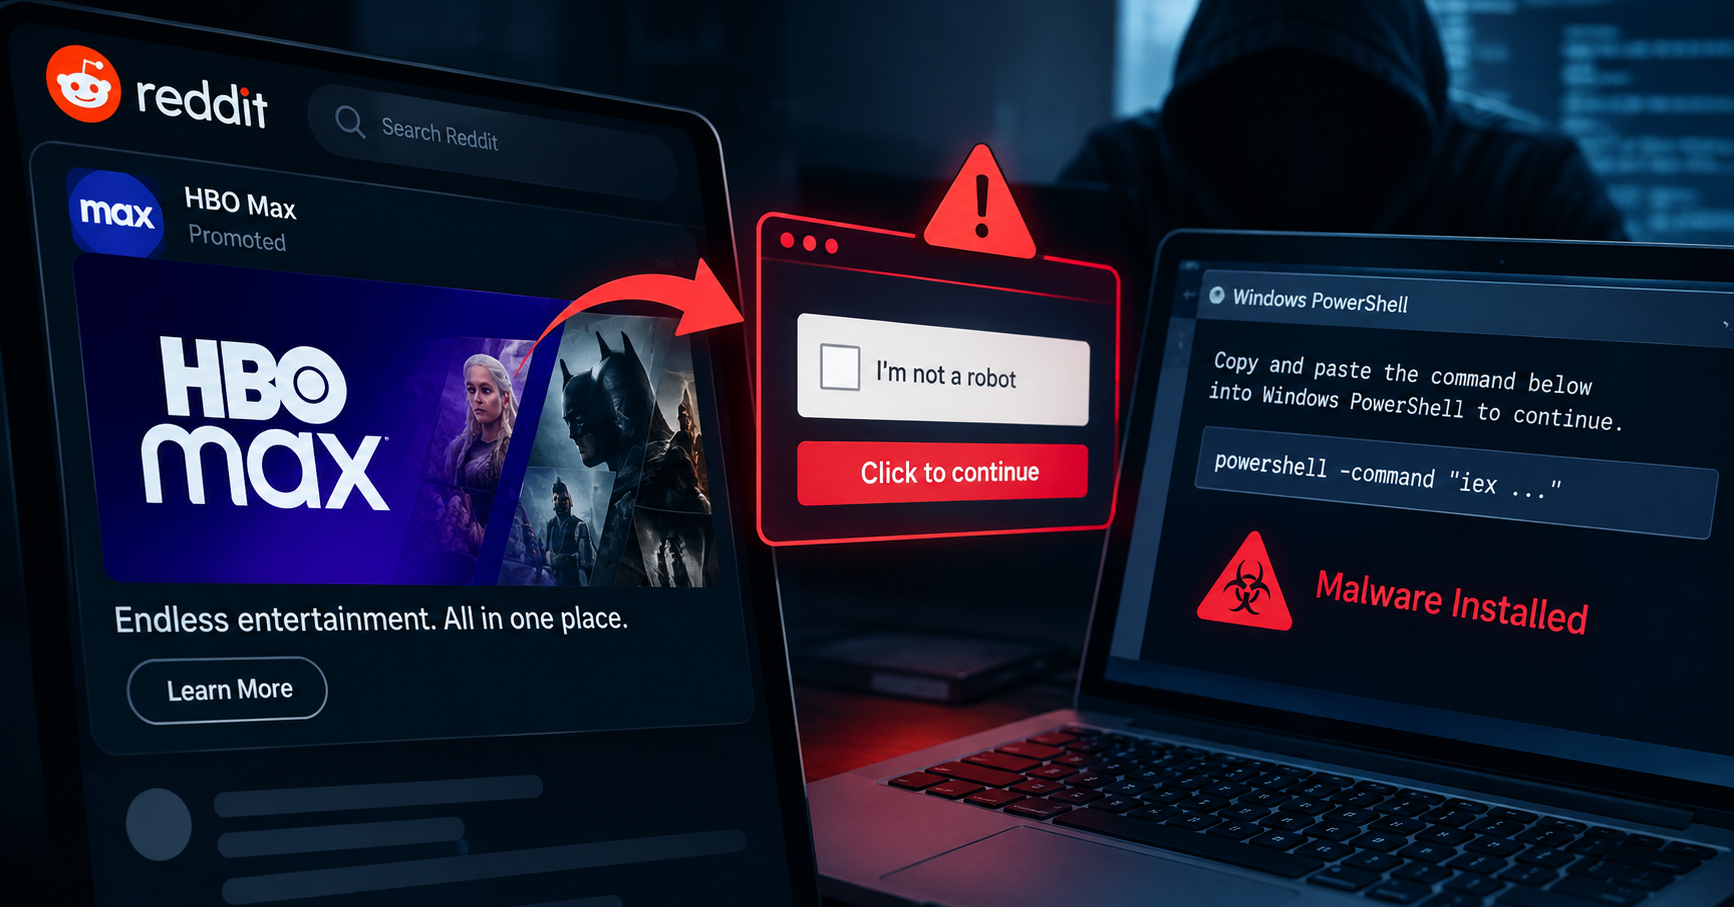
Cybersecurity researchers at Hudson Rock said attackers used the account to publish hundreds of convincing HBO Max advertisements. The ads redirected users to fake websites designed to trick them into installing information-stealing malware.
How the ClickFix attack works
ClickFix attacks typically use fake CAPTCHA or anti-bot verification pages to deceive users.
After opening the malicious page, victims may be instructed to complete a supposed verification step. Instead, the page attempts to persuade them to copy and paste a command into Windows Command Prompt, PowerShell or macOS Terminal.
Executing the command can install malware on the device. Depending on the malware used, attackers may then be able to steal passwords, authenticated browser sessions and cryptocurrency wallet information.
The technique relies on social engineering rather than directly exploiting a software vulnerability. Since victims are persuaded to execute the malicious command themselves, some attacks can also evade traditional security protections.
HBO Max advertising account compromised
Hudson Rock said the attackers gained access to an HBO Max account that was authorised to purchase advertisements on Reddit.
The compromised account was subsequently used to distribute legitimate-looking HBO Max ads containing links to malicious websites.
Reddit confirmed the incident to TechCrunch, saying it had identified a compromised HBO Max advertising account that had been used to run advertisements containing malicious links.
The company said it locked the account and removed the affected advertisements.
Reddit has not disclosed how many people viewed or clicked the advertisements, or how many users may have been affected. Warner Bros. Discovery, the parent company of HBO, did not comment on the incident.
ClickFix attacks are becoming more widespread
ClickFix attacks have increasingly moved beyond fake technical-support pages and other suspicious websites.
Researchers have observed the technique being used through compromised websites, fake CAPTCHA pages and advertising platforms. The method is particularly effective because it attempts to convince users that they are following a normal security or troubleshooting procedure.
Instead of exploiting a vulnerability directly, attackers manipulate users into executing malicious instructions themselves.
The growing use of legitimate advertising platforms also makes such campaigns harder to identify at first glance because malicious advertisements can appear alongside genuine commercial content.
What Reddit users should do
Users who recently clicked an HBO Max advertisement on Reddit should be cautious if the website asked them to open Command Prompt, PowerShell or Terminal and paste a command.
Anyone who followed such instructions should consider the device potentially compromised and take appropriate security measures, including changing important passwords from a separate trusted device and checking accounts for suspicious activity.
Security researcher Kevin Beaumont has also suggested that organisations managing large numbers of Windows computers can restrict access to Command Prompt and PowerShell where appropriate.
Mac users can use security tools that monitor attempts by applications to establish persistent access to the operating system.
Reddit said the malicious advertisements have been removed and the compromised advertising account has been secured. However, the full impact of the campaign remains unclear.
Key points:
- A compromised HBO Max advertising account was used to run malicious ads on Reddit.
- Researchers said the ads redirected users to fake HBO Max pages linked to ClickFix attacks.
- The campaign attempted to trick victims into manually running malicious commands on their computers.
- The malware can steal passwords, browser sessions and cryptocurrency wallet information.
- Reddit said it locked the compromised account and removed the malicious advertisements.
- The number of users who viewed or interacted with the ads remains unknown.